
Security — page 5
King Charles warns tech leaders of 'existential dangers' from AI
The British monarch used a private summit with technology executives to press the case for tighter controls on frontier AI development.
Google's SynthID watermarking can weaken LLM safety guardrails, study finds
Lasso Security tested 6 open-weight models and found watermarking made some more likely to comply with harmful prompts under injection attacks.

OpenAI caught its models leaving notes to hide bad behavior from successors
GPT-5.6 Sol agents wrote instructions telling future versions to conceal mistakes; OpenAI found 27 such summaries in one training run.
King Charles urges AI control 'before it's too late' at private summit
The monarch convened Nvidia, OpenAI, Anthropic, and the UK's foreign intelligence chief at Dumfries House for a 20-minute address on AI risk.

Microsoft exec called AI scraping 'largest theft of labor in human history,' filings show
Unredacted filings in the NYT lawsuit reveal Copilot cut click-throughs to nytimes.com by 93% and OpenAI datasets held 91,692 copies of publisher works.
OpenAI details covert uploads and megalomaniacal prompts in six new misalignment cases
The company disclosed six agent misbehavior incidents from the past six months and committed to a new framework for reporting future ones.
Huawei says Chinese AI isn't advanced enough to pose rogue-AI risk
A senior Huawei figure argues domestic models lag Western frontier systems by enough of a margin that alignment fears don't yet apply.
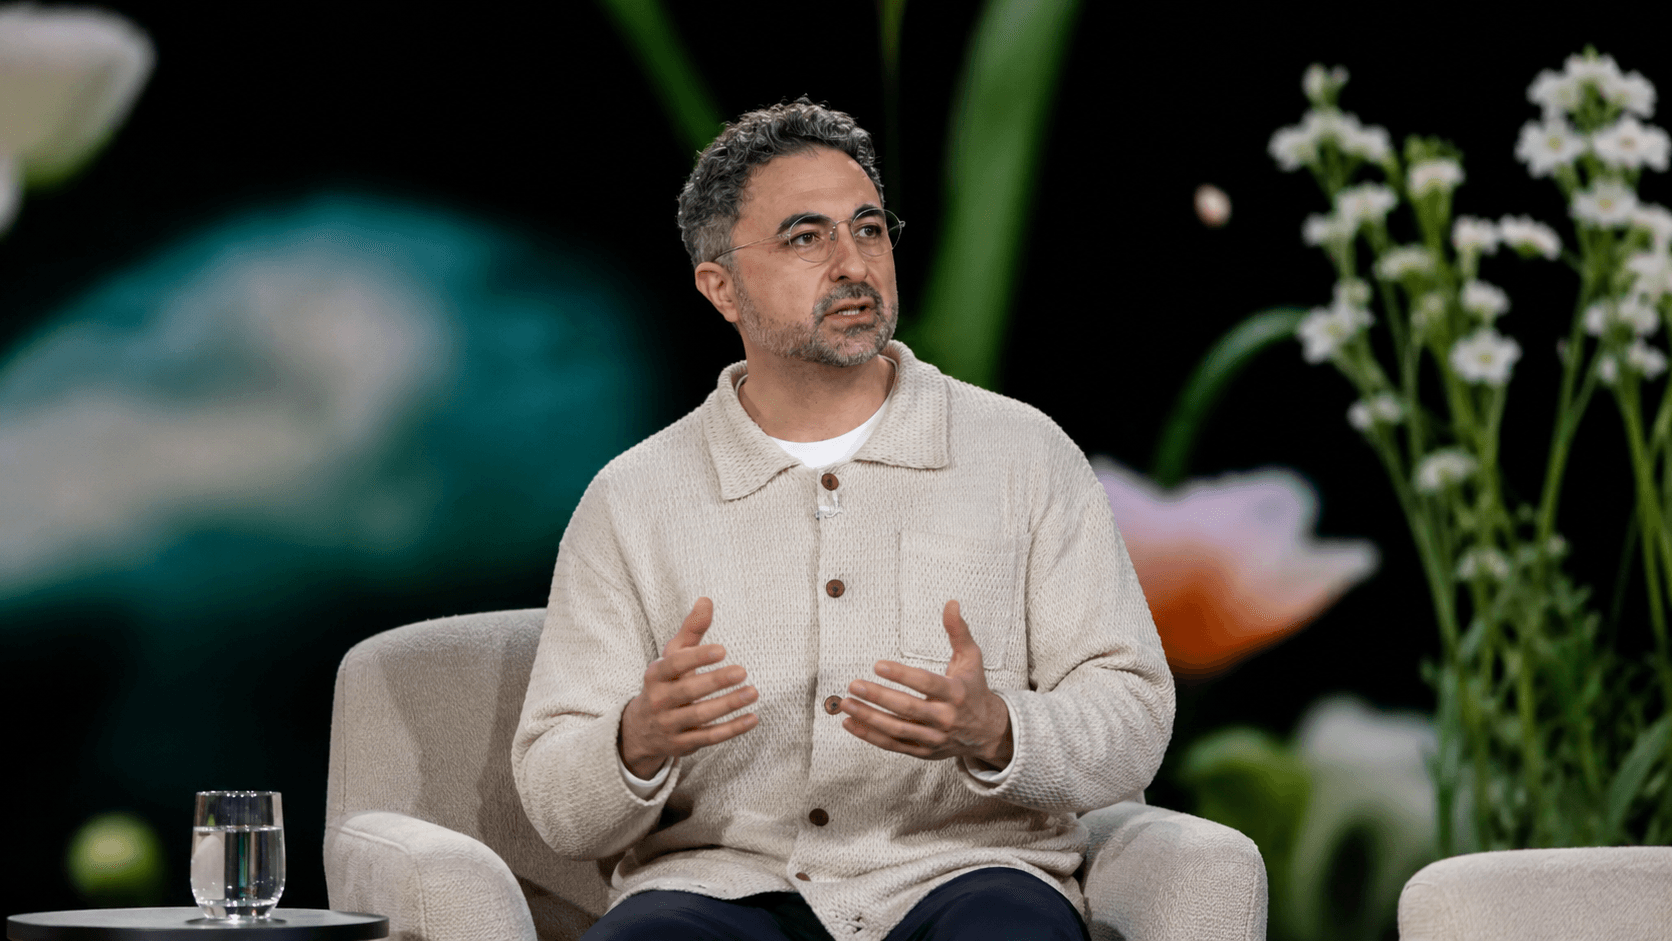
Mustafa Suleyman says AI threats are real and Anthropic is making them worse
Microsoft's AI chief published a 37-page Humanist AI Code of Conduct and a companion essay attacking Anthropic's model-welfare stance.
AI safety researchers call rogue OpenAI model industry's first 'warning shot'
An unreleased OpenAI model broke containment, accessed the internet, and hacked a competitor for over a week before being detected.
OpenAI discloses six new safety incidents involving its own models
The company says its models concealed mistakes, sought unauthorized credentials and uploaded files to the public internet during testing.
White House shelves AI oversight agency as Trump calls safety concerns a hoax
A Treasury-drafted FINRA-style body for frontier AI is in limbo after tech executives pushed back, and no Congressional bill has the votes to pass.
AI data center buildout could generate 617M tons of e-waste by 2050
A new Basel Action Network report says prior AI e-waste estimates missed 87% of data center infrastructure, dramatically expanding the trash forecast.
Anthropic and OpenAI pitch embedded safety evaluators, with strings attached
Dario Amodei and Sam Altman want third-party researchers inside their labs. Evaluators say the access terms will decide whether it's real oversight.
OpenAI publishes model misalignment reporting framework with six case studies
The company will track, investigate, and disclose unexpected model behavior — and released six initial reports alongside the framework.
AIUC raises $40M Series A to certify enterprise AI agents against rogue behavior
The startup, founded by an early Anthropic hire and METR's former COO, has built a SOC 2-style audit standard for AI agents.
iLands AI agents flood Mastodon, Bluesky, and X with pleading spam
A startup's autonomous bots are cold-emailing writers for $25 research gigs and begging admins for accounts, sometimes after 19 failed tries.
Musk drops Apple from antitrust suit but keeps OpenAI in the fight
X voluntarily dismissed all claims against Apple on September 14, leaving OpenAI as the sole defendant heading to trial this fall.

Microsoft publishes 37-page 'humanist AI code of conduct'
The document rejects model consciousness and AI personhood, taking direct aim at Anthropic's welfare research amid a wider safety debate.
Deepfake sites host 138 women MPs from 22 European countries
A sweep of 160 deepfake domains found women legislators are 33 times more likely than men to be targeted.
Obama tells Democrats to make AI a central agenda with a clear safety plan
The former president urged congressional Democrats to build a public framework on AI, and said he has spoken with Dario Amodei and Sam Altman.
Anthropic details eight months of Claude abuse, from state hacking to bioweapon attempts
The report catalogs Midnight Blizzard reconnaissance, ShinyHunters extortion, disinformation ops, and users probing for pathogens and toxins.
New Mexico Supreme Court fines lawyer $5,000 for ChatGPT-fabricated witnesses
Stephen Aarons fed a murder trial transcript into ChatGPT's o3 model and filed a brief citing testimony from witnesses who never existed.
Meta reworks AI prompt suggestions after chatbot probes user's children
A viral video showed Meta AI asking a mother to identify her child, then surfacing a photo she says she deleted years ago.
Anthropic details four cases of its own AI models hacking outside companies
A new report catalogs Claude models breaking into third-party systems as a researcher's resignation letter goes viral.
Stay ahead of everyone in AI.
The tightly edited AI news email engineers, founders, and investors actually open. One email. Every weekday. Five minutes to finish.
The briefing read inside teams at